Behind the 11.8 billion dollar North Korean hacker business, the asymmetric offense and defense battle has entered the AI era
 Core Viewpoint

 Resource advantages no longer mean absolute security; the real danger lies in responding to the threats of the new era with the thinking of the old era.
Author: Nancy, PANews
The world is entering an era of asymmetric warfare.
On the physical battlefield between the U.S. and Iran, Iran is engaging in a war of attrition using low-cost drones, missiles, and maritime blockades to constrain U.S. military resources at relatively limited costs, while exerting pressure on the global economy.
In the cryptocurrency world, AI is lowering the technical threshold for cyberattacks, amplifying the efficiency and destructive capability of attackers. Attackers may only need to invest limited resources to cause significant losses to large enterprises and complex systems.
$11.8 billion, a national-level hacker legion
North Korean hackers frequently launch attacks, causing panic in the cryptocurrency market. Some are busy reinforcing security defenses, while others are taking alternative approaches. A developer recently designed a rather unconventional verification mechanism in an attempt to spiritually prevent North Korean users from accessing the website. Unexpectedly, this security experiment with a humorous twist inadvertently attracted a real cyberattack.
From high-frequency keywords in security incidents to materials for jokes in the cryptocurrency community, North Korean hackers are gradually becoming an unavoidable topic in the industry. Behind the jokes lies a growing concern about cybersecurity risks in the market.
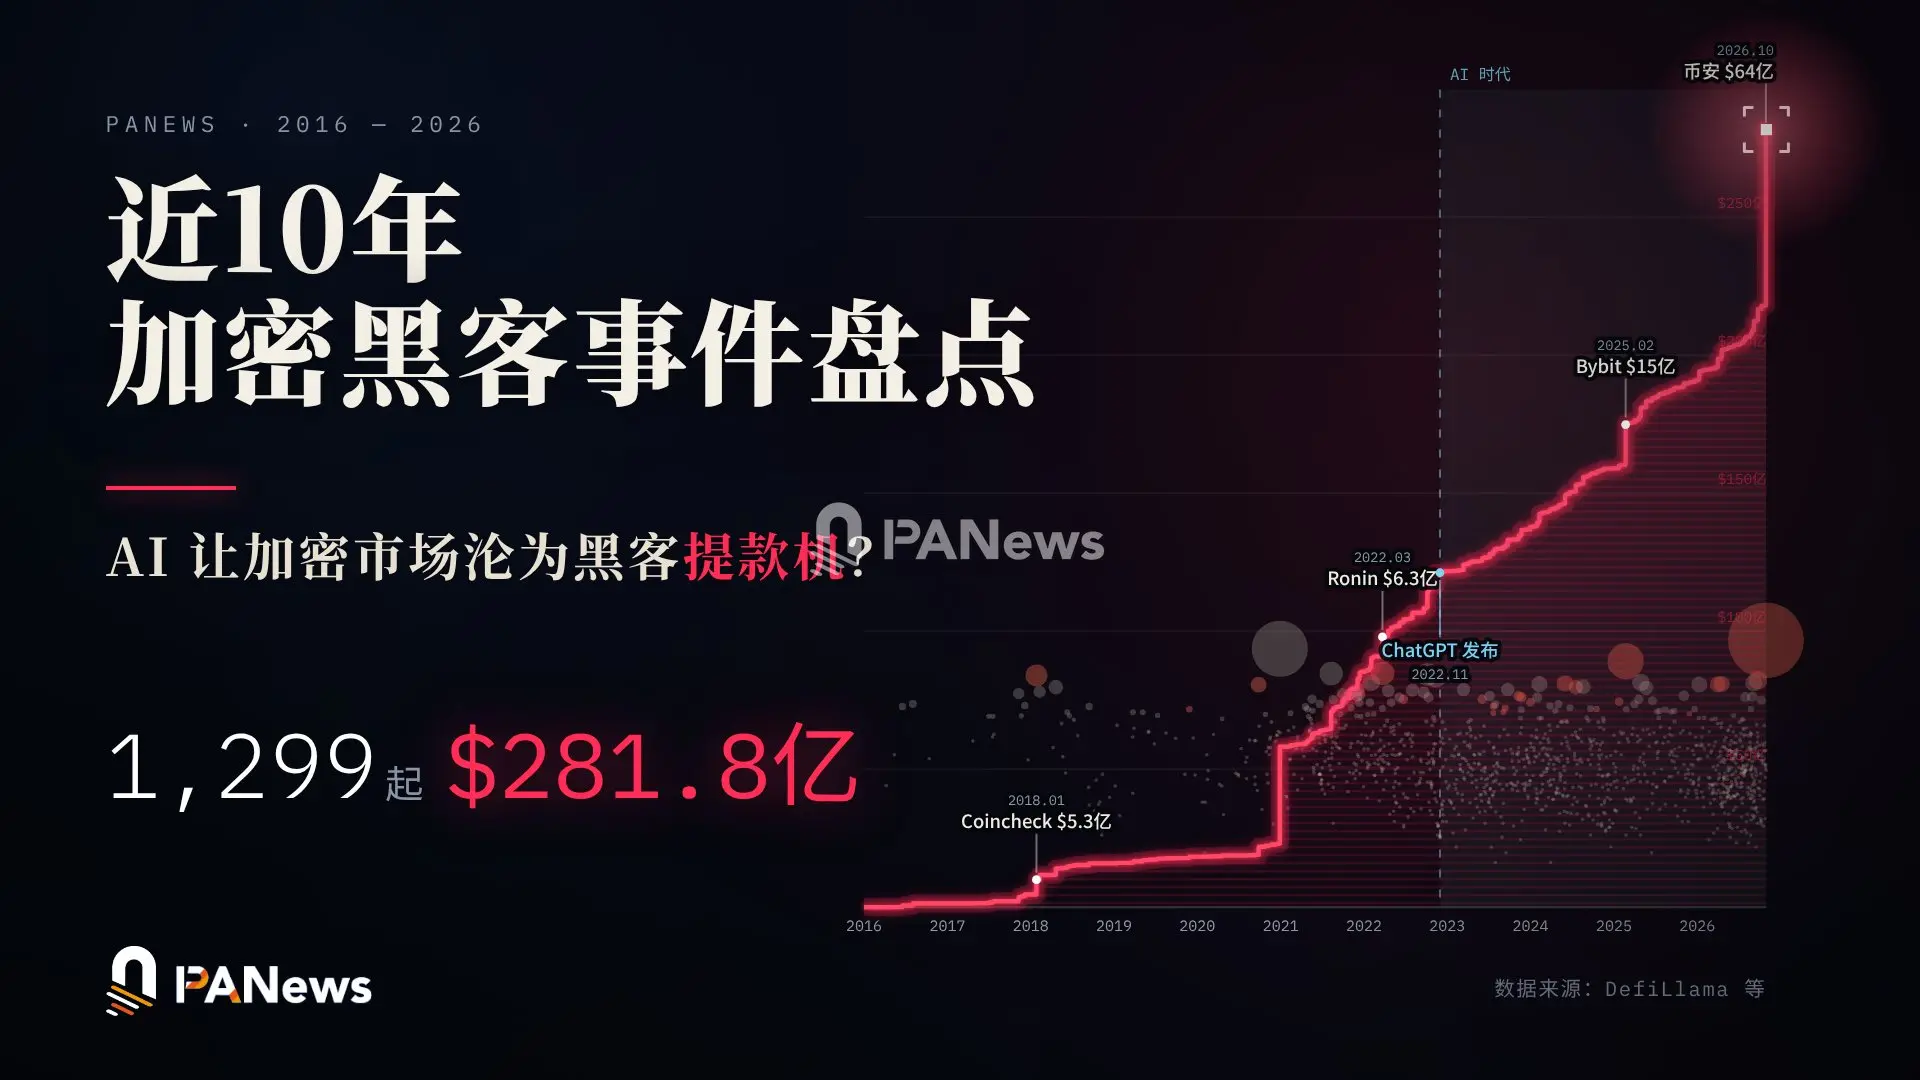
Data from Chainalysis shows that as of October 29, 2026, losses from suspected North Korean-related hacker attacks account for nearly 89% of the reported losses from cryptocurrency hacker attacks this year, compared to 15% in 2021. In terms of losses from individual attacks, the average loss from suspected North Korean-related attacks has risen from $50.65 million in 2021 to about $185 million in 2026, approximately 3.7 times that of 2021.
As one of the countries long subjected to international sanctions, North Korea finds it difficult to obtain foreign exchange and resources through normal international trade and financial activities. Cyberattacks have thus gradually become an important means for it to acquire funds and evade financial restrictions.
North Korea's hacking force is not a group of technical experts fighting individually, but rather a highly organized national-level cyber operation system built over a long period. From talent selection and elite education to military training, followed by overseas infiltration and practical operations, North Korea has established a relatively complete talent cultivation and operational mechanism.
This mechanism resembles a pyramid selection process for math Olympiad participants. It identifies a few outstanding youths with exceptional logical thinking and mathematical talent from across the country while also reviewing their political backgrounds and loyalty. Selected talents can access concentrated educational resources and receive long-term, systematic training in computer science, mathematics, and programming.
After completing domestic training, some personnel are sent overseas to work under identities such as students, IT professionals, or remote technicians, accumulating technical experience in real environments while learning the language, culture, and work habits of the target country to prepare for subsequent operations.
To attract and retain these technical talents, North Korea offers special benefits, including exemptions from certain military obligations, residency qualifications in the capital, housing, higher income, and better educational and medical resources. For a resource-limited country, these incentives are quite appealing. Hackers with scarce skills thus gain a special social status, gradually becoming a new privileged group within North Korea.
Talent cultivation is just the first step; the highly specialized organizational division of labor is the real ace up North Korea's "keyboard warriors." Reconnaissance personnel are responsible for gathering global cyber intelligence and identifying system vulnerabilities to filter targets for attack operations; operational personnel use identity disguise, social engineering, and malware to implement infiltration, stealing funds and sensitive information; there are also dedicated personnel responsible for fund transfers, money laundering, and asset liquidation, converting the proceeds from cyberattacks into disposable funds.
From target selection and technical infiltration to fund transfer, a seemingly simple cryptocurrency asset theft incident may involve a complete cross-border operational chain. Lazarus Group, APT38, Kimsuky, etc., are different North Korean-related hacker organizations identified by external security agencies based on their attack targets, technical methods, and behavioral characteristics.
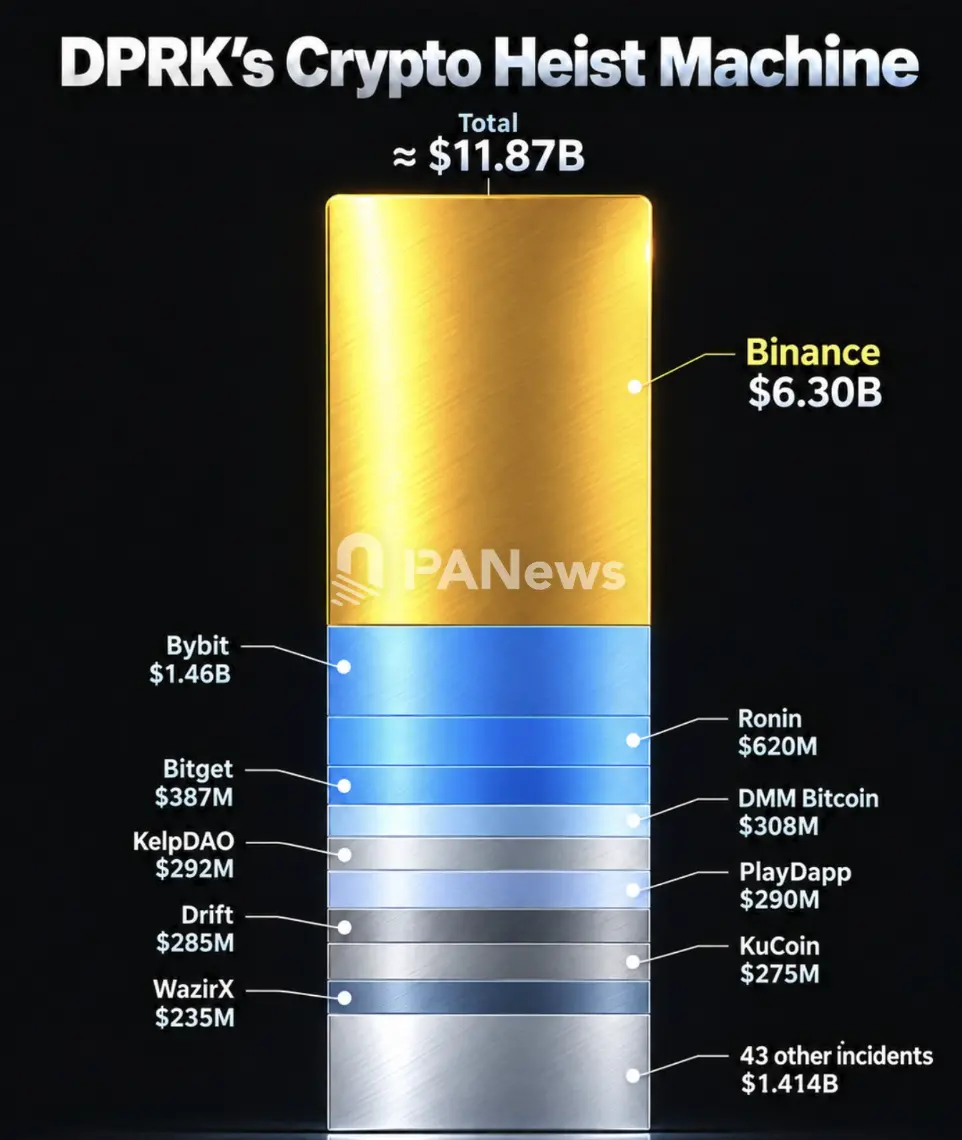
According to analyst Darkfost's recent disclosure, with the occurrence of attacks on Binance, the total amount of funds stolen by the Lazarus organization has reached $11.87 billion. According to data from the Bank of Korea in 2025, this figure is equivalent to 45% of North Korea's GDP and 35% of its Gross National Income (GNI). If this estimate holds, the proceeds from cyberattacks would no longer just be additional illegal income but could become a significantly substantial source of funds within North Korea's economic system.
For North Korea, cyberattacks are both a strategic weapon and another channel to bypass financial blockades and acquire economic resources. A country that is difficult to reach through traditional financial systems is seeking new ways to obtain resources in cyberspace.
The biggest security vulnerability may be the "colleagues" around you
When attackers no longer attempt to break through firewalls head-on but instead choose to find entry points from within the organization, the cost of attacks is often lower, and the concealment is stronger. Traditional defense systems relying on security devices and network boundaries are facing new challenges.
North Korean hackers are taking this asymmetric attack method to the extreme. They impersonate IT professionals or job seekers by fabricating resumes, forging passports, and identity information, actively contacting core employees such as developers and operations personnel within companies.
To further lower the target's guard, attackers may even participate in real video interviews and provide fake social media accounts containing personal photos and daily updates, striving to create a believable job seeker image. Once they pass through the recruitment process and enter the team, they may leverage their legitimate employee status to remain hidden for a long time, gradually accessing internal systems, code repositories, and sensitive permissions, seeking further penetration opportunities.
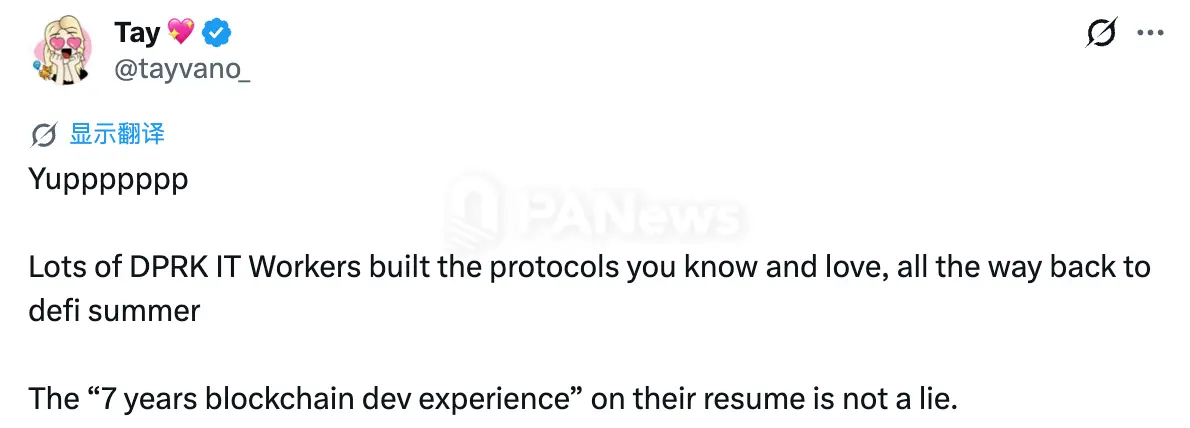
The Ketman project funded by the Ethereum Foundation identified 100 North Korean IT personnel infiltrated in Web3 organizations within six months. MetaMask security researcher Taylor Monahan previously revealed that at least 40 DeFi protocols have employed North Korean IT personnel during their development, spanning a period of up to seven years. These individuals entered Web3 teams by forging passports, visas, and meticulously crafted resumes. More confusingly, some of their blockchain development experience is genuine.
According to Binance's latest disclosure, this year, the platform has intercepted 57 suspected cyberattacks related to North Korea. Attack methods include infiltration through fake job interviews, using malware disguised as commonly used developer tools, tampering with software packages and browser plugins, and impersonating video conferencing applications to induce employees to run malicious programs, as well as stealing credentials through social engineering attacks and implanting remote control trojans.
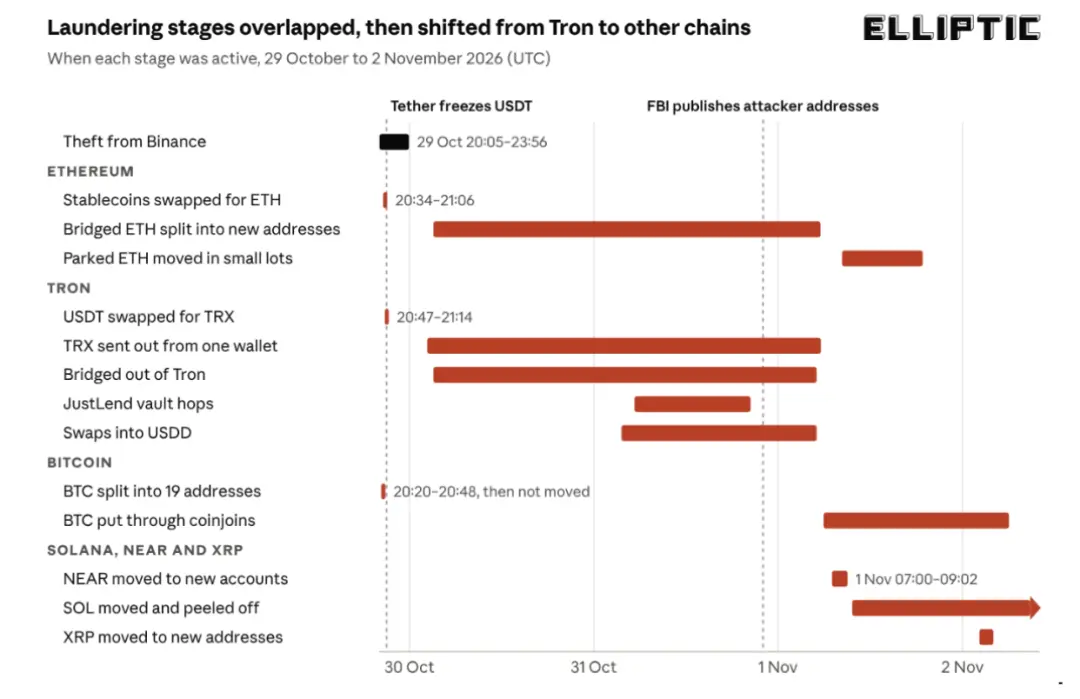
In the recent Binance theft incident involving over $6 billion, according to the initial investigation information disclosed by officials, attackers contacted a software engineer from Binance's wallet infrastructure team through fake high-salary job offers. After several rounds of video interviews, the attackers induced the engineer to run malware disguised as a technical test project on their work computer, ultimately gaining control of the employee's device and further threatening the security of the wallet infrastructure. The founder of SlowMist, Yu Xian, pointed out that such incidents belong to advanced persistent threats (APT), involving human exploitation, intelligence reconnaissance, malware evasion, trust chain exploitation, targeted lateral poisoning, cloud environment infiltration, risk control bypass, and 0-day vulnerabilities.
Similar tactics have precedents. In 2022, when the Ronin Network under Axie Infinity was attacked, the North Korean-related hacker organization Lazarus Group also contacted a senior engineer from Sky Mavis via LinkedIn with high-paying job offers. After several rounds of interviews, the attackers sent a fake job invitation file containing a trojan, ultimately controlling the systems related to the validation nodes and stealing approximately $625 million in assets.
This is the asymmetric security dilemma facing the cryptocurrency industry. In the past, security defenses relied more on building solid technical barriers; however, as social engineering attacks continue to evolve, attackers do not necessarily need to master more advanced technologies or possess more resources, but only need to find a weak link.
Compared to technical vulnerabilities, what is truly difficult to guard against may be those who have already gained trust.
AI upgrades the offensive and defensive battleground, the resource competition has already begun
If social engineering attacks have lowered the cost for hackers to breach organizational defenses, the continuous iteration of AI has further amplified the scale and efficiency of cyberattacks.
The latest report from Microsoft's threat intelligence team indicates that among the eight major North Korean hacker organizations they track, three have deeply integrated AI tools into their daily attack processes, reaching the highest level of Microsoft's cyber threat AI application maturity model.
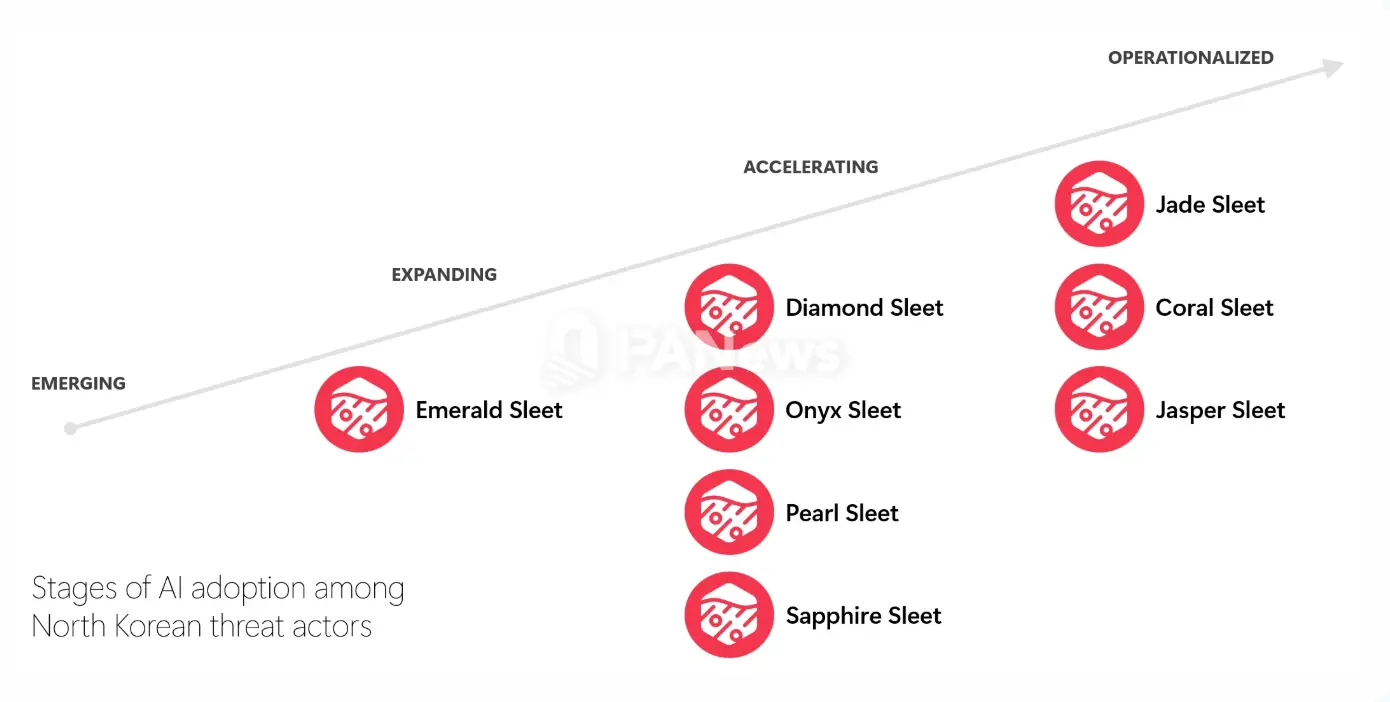
In terms of social engineering and identity forgery, North Korean hacker organizations utilize AI to generate phishing, recruitment, and investment bait content in bulk, impersonating foreigners through translation and tone adjustments, and even generating fake resumes, interview responses, avatars, and voice videos. One organization generated over 100 customized phishing PDF files targeting South Korean users between August and September 2026. North Korean remote IT personnel employed by overseas companies have also begun to use AI to maintain multiple identities simultaneously.
According to South Korean security firm Genians, the North Korean hacker organization Kimsuky has built a local large language model (LLM) and RAG environment this August, leaving behind numerous records of using the AI code editor Cursor. After relevant tools were intercepted, they could quickly switch tools to continue their activities.
Microsoft believes that these organizations have not yet achieved fully autonomous attacks, and the actual impact of AI on attack success rates and costs remains unclear. However, from target reconnaissance and social engineering to identity forgery and malware development, AI has entered multiple stages of the attack process. It may not directly turn ordinary attackers into top hackers, but it can compress the time and manpower required to complete complex attacks.
In the Binance hacking incident, AI tools also became part of the attack. According to investigative information, attackers provided engineers with tampered AI programming tools through a supply chain attack. Even if engineers switched tools after discovering anomalies, their job information and that of other members of the wallet infrastructure team had already been exposed. Subsequently, after gaining control of one engineer's computer, attackers further infiltrated other employees' devices using Binance's internal AI tools, ultimately gaining signature control.
As AI capabilities continue to enhance, the competition between cyber offense and defense is also extending from traditional competition in technology and talent to a struggle for data, models, and computing power resources, further exacerbating the asymmetry in cyber offense and defense.
Recently, security researcher Jun Song shared that an anonymous black hat organization contacted him, hoping to commission him to use exploit data to conduct reinforcement learning on open-source weight models, and they were willing to pay a very high reward. Jun Song stated that the other party claimed the scale of the attack data was something he had never seen before; even if someone told him it was an undercover dataset from law enforcement, he would believe it. In contrast, a white hat project he participated in used GLM-5.3, and the amount of data used was less than 1% of what the other party claimed, yet the model's performance had already significantly surpassed that of cutting-edge models.
In the AI offense and defense competition, high-quality, large-scale exploit data may become an important resource for training cybersecurity models. Whoever can obtain more data, stronger models, and more sufficient computing power may gain an advantage in future offense and defense competitions.
If massive exploit data can be effectively transformed into model capabilities, attackers may further improve the efficiency of vulnerability discovery and attack execution. Correspondingly, whether defenders can obtain sufficient data, models, and computing power will also affect their ability to identify and respond to new threats.
Coinbase disclosed in June that it had obtained access to the cutting-edge model Claude Mythos from Anthropic and would use it to strengthen the security defenses of cryptocurrency wallets and assets. In contrast, months later, Binance still stated that it had not obtained similar access. The differences in access to cutting-edge models may further widen the capability gap among different companies in vulnerability discovery, automated security auditing, and risk defense.
From Iran using low-cost weapons to constrain U.S. military power, to North Korean hackers accelerating attacks through identity disguise, social engineering, and AI tools, although the battlefields are different, they point to a reality: resource advantages no longer mean absolute safety; the real danger lies in responding to new era threats with old-era thinking.
 Risk warning
 Risk warning