BTC $81,521.83 +0.41%
ETH $2,403.88 +1.03%
BNB $745.04 +2.36%
XRP $1.31 -0.19%
SOL $104.37 +0.65%
TRX $0.3293 +0.37%
DOGE $0.0796 +1.69%
ADA $0.2151 +1.39%
BCH $286.11 +4.46%
LINK $12.03 +1.07%
HYPE $78.33 +1.42%
AAVE $147.94 +1.63%
SUI $0.9884 +1.21%
XLM $0.1761 +0.27%
ZEC $1,247.32 +4.33%
AAPL $346.37 -0.05%
AMZN $249.29 -0.77%
GOOGL $322.83 -1.10%
MSFT $524.90 +0.08%
META $645.12 -0.53%
NVDA $211.91 -0.59%
TSLA $371.33 -2.04%
SNDK $1,268.47 +0.72%
INTC $86.71 +0.06%
SPCX $147.08 +0.06%
MU $884.18 +2.00%
AMD $516.54 +0.74%

onekey

All
Article
Flash

OneKey stops adding new distributors and offers free upgrades for CryptoBilis users

The founder of the hardware wallet brand OneKey, Yishi, stated that recently multiple users who purchased Ledger hardware wallets through CryptoBilis reported asset theft. Ledger has confirmed that affected devices were implanted with unauthorized hardware, and the cause and scope of the impact are still under investigation. Since CryptoBilis also sold hardware wallets from brands like OneKey, OneKey has terminated its authorized dealer qualifications and will stop adding new dealers effective immediately.OneKey will re-evaluate existing dealers, and those who cannot verify the operating entity or ultimate beneficiaries will have their authorization canceled. A complete list of authorized dealers will be published after the review is completed. From March 1, 2026, to the date of this announcement, users who purchased OneKey hardware wallets through CryptoBilis, regardless of model, activation status, or usage, can apply for a free replacement. If the original model is in stock, a brand new device of the same model will be provided; if out of stock, a free upgrade will be given, shipped directly from the official OneKey store without the need to return the old device. Applications will be accepted until December 31, 2026, and must be submitted through OneKey's official website customer service or help.onekey.so with proof of purchase, device model, and usage status.OneKey reminds users that unactivated devices should refrain from activation and apply for a replacement directly; users who have used the device and have assets should proactively treat the old mnemonic phrase as potentially compromised, and transfer assets to a wallet created with a brand new mnemonic phrase as soon as possible, and should not import the old mnemonic phrase into a new device.

first_img OneKey reproduces the transaction replacement attack targeting the old version of the Ledger Ethereum application

The security team of the open-source wallet provider OneKey successfully replicated the exploitation of a vulnerability in the old version of the Ledger Ethereum application in a laboratory environment. OneKey's founder and CEO Wang Yishi stated that they executed a "transaction replacement attack" on Ledger Ethereum application version 1.22.1 by exploiting a previously patched vulnerability, allowing attackers to overwrite pending transactions while users review legitimate transactions.Ledger responded that exploiting this vulnerability requires controlling the communication between the device and the host, such as through malware, compromised wallet software, or malicious web pages. Ledger has added application layer protections in the Ethereum application version 1.22.2 released on August 13 and fixed the underlying issue in Secure SDK 26.6.1 on August 21. Ledger emphasized that no users were hacked as a result; this was merely a replication of the vulnerability in a laboratory environment.This security test occurred after the Coldcard vulnerability incident. Previously, the Coldcard wallet had a firmware vulnerability that posed security risks to some mnemonic phrase generation, but Ledger stated that its devices were not affected by this vulnerability because recovery phrases are generated by a certified random source built into the device's secure chip. The vulnerability replicated by OneKey is unrelated to mnemonic phrase generation but affects the way transactions are processed during the signing process.

OneKey founder Yishi spoke out about the Resupply attack incident, calling on projects like Curve to refund user losses

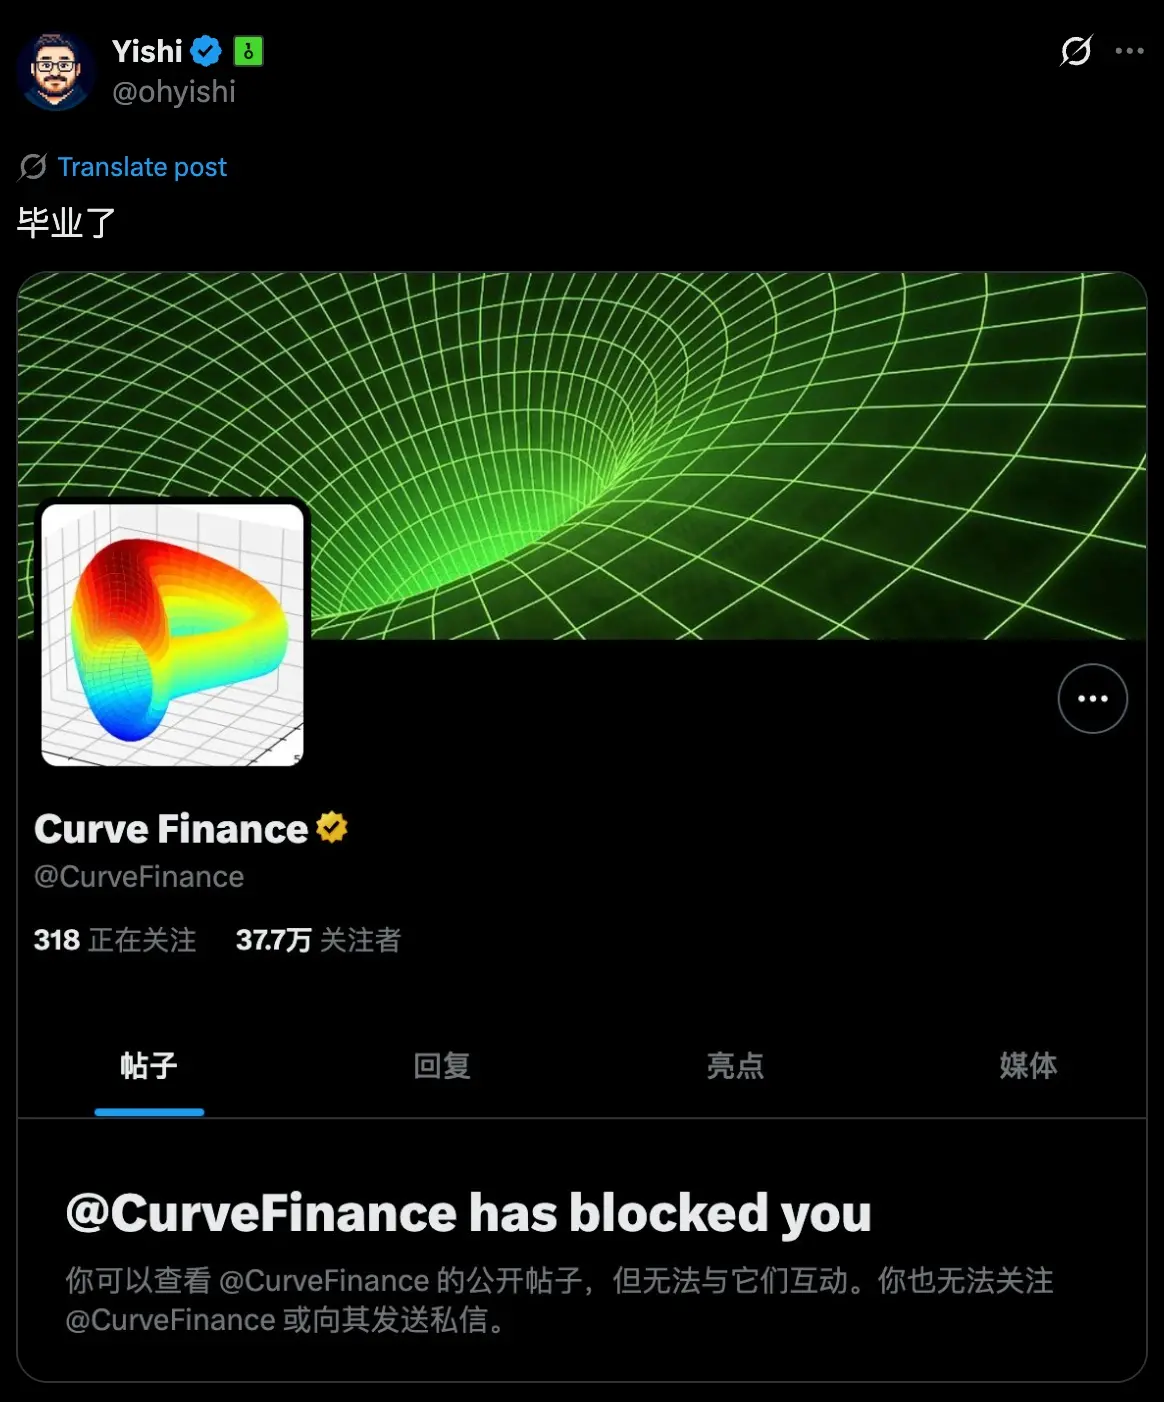
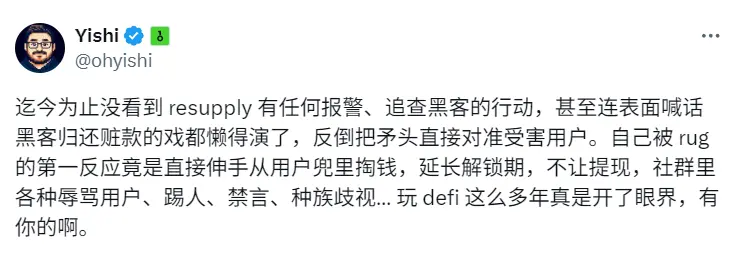
ChainCatcher news, OneKey founder Yishi publicly stated about "Curve ecosystem DeFi protocol Resupply suffering a price manipulation attack resulting in a loss of $9.6 million," demanding that Curve provide a fair solution for every investor and return the user funds lost due to serious technical errors by the project team.Yishi revealed that he is one of the three major investors in Resupply, and the losses from this incident amount to millions of dollars. He accused the team of banning reasonable questioners on Discord and lacking the necessary accountability. He emphasized that the vulnerability stemmed from the failure to destroy the initial shares when deploying the ERC4626 vault, allowing attackers to mint shares at almost zero cost and drain the vault, which constitutes a protocol-level design and deployment error.Yishi stated that it is unreasonable for the Resupply team to shift the losses onto the insurance pool depositors, as the insurance pool is meant for black swan events and market fluctuations, not to cover the team's technical negligence. He also pointed out that Curve, Convex, and Yearn had participated in supporting Resupply in various forms and had gained actual benefits from it, and should not shirk responsibility afterward. He called for the relevant parties to bear the necessary costs and return user assets.In response to the incident, Curve stated this morning, "Although Resupply was not developed by the Curve team, its creators are experienced, and we believe they will do their best to address the issue. The insurance pool is intended to provide protection for such security incidents, and any recovered assets should be prioritized for processing."
app_icon
ChainCatcher Building the Web3 world with innovations.